1. Overview of load balancing in Foreman
You can configure your Foreman environment to use a load balancer to distribute host requests across multiple Smart Proxy servers. This improves performance and keeps host connections working when one Smart Proxy server is unavailable.
1.1. Components of a load-balanced setup
When you configure your Foreman environment for load balancing, several components interact to distribute traffic and provide high availability.
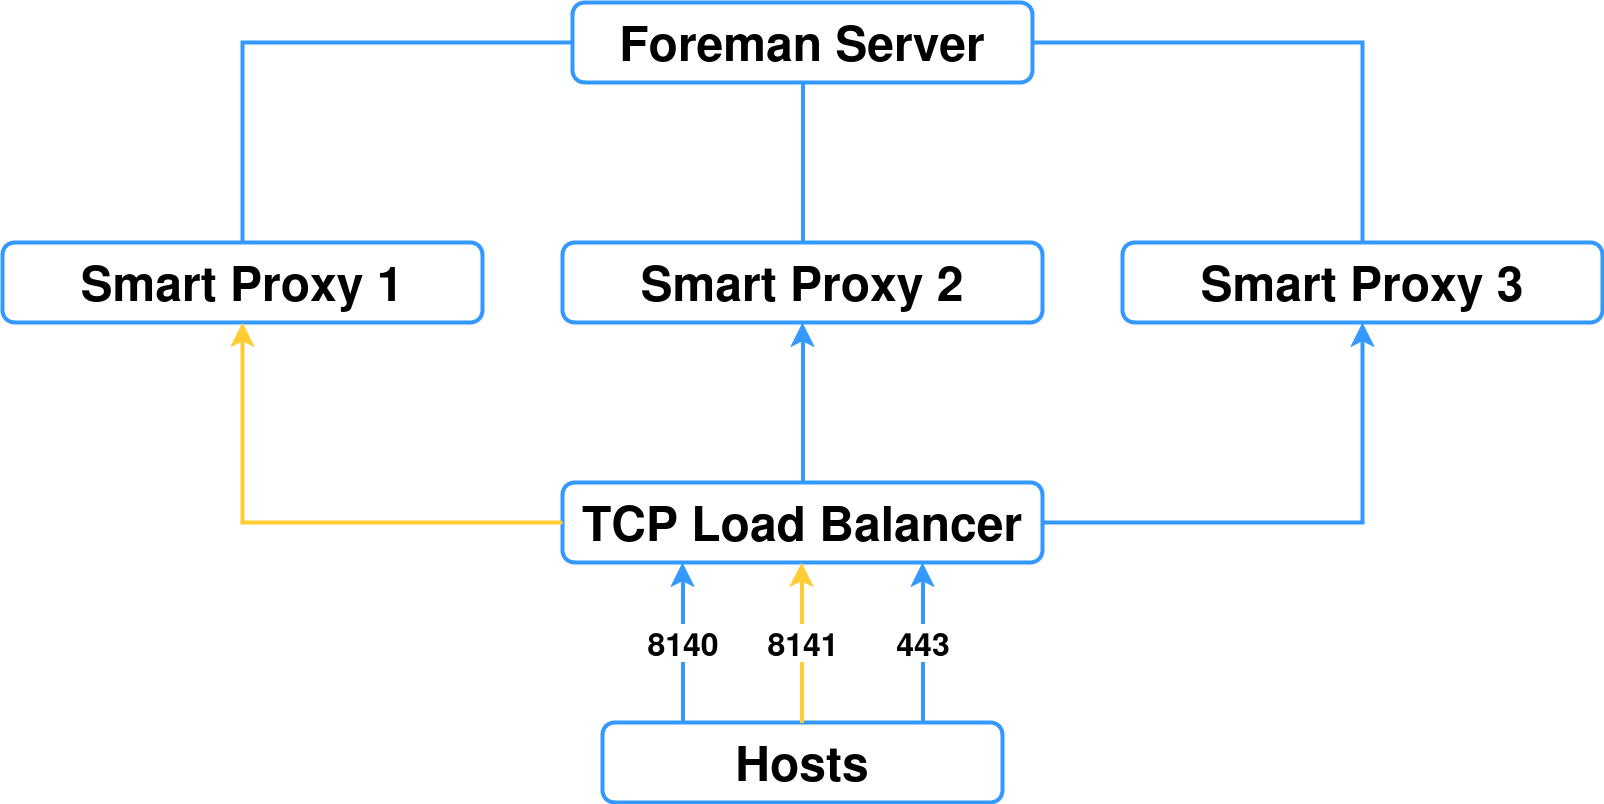
A load-balanced setup in a Foreman environment consists of the following components:
-
Foreman server
-
Two or more Smart Proxy servers
-
A load balancer
-
Multiple hosts
A host sends a request to the TCP load balancer. The load balancer receives the request and determines which Smart Proxy server will handle the request to ensure optimal performance and availability.
1.2. Services and features supported in a load-balanced setup
A load balancer in Foreman distributes load only for selected services and features. The services listed below are supported for load balancing and will continue to work when one Smart Proxy server is unavailable.
The following services and features are supported for load balancing:
-
Registering hosts
-
Providing content to hosts
-
Configuring hosts by using Puppet
Other Foreman services, such as provisioning, virt-who, or remote execution, go directly through the individual Smart Proxies on which these services are running.
1.3. Additional maintenance required for load balancing
Configuring Smart Proxies to use a load balancer results in a more complex environment and requires additional maintenance.
The following additional steps are required for load balancing:
-
You must ensure that all Smart Proxies have the same content. If you publish a content view version on Foreman, synchronize it to all Smart Proxy servers.
-
You must upgrade each Smart Proxy in sequence.
2. Preparing Smart Proxy servers for load balancing
Before you can configure load balancing in your Foreman environment, you must install a new Smart Proxy server. This is the Smart Proxy server that you will later configure for load balancing.
|
Important
|
Foreman does not support configuring existing Smart Proxy servers for load balancing. You must create a new Smart Proxy server for this purpose. |
2.1. Registering Smart Proxy server
Register the base operating system to Foreman server to access Smart Proxy server installation packages.
2.1.1. Prerequisites for registering Smart Proxy server to Foreman server
Your environment must meet the following requirements before you can register your Smart Proxy server to your Foreman server.
-
Prerequisites for Red Hat subscription manifest:
-
On Foreman server, a manifest must be installed and it must contain the appropriate repositories for the organization you want Smart Proxy to belong to.
-
The manifest must contain repositories for the base operating system on which you want to install Smart Proxy, as well as any clients that you want to connect to Smart Proxy.
-
The repositories must be synchronized.
For more information on manifests and repositories, see Managing Red Hat Subscriptions in Managing content.
-
-
Prerequisites for host registration:
-
An activation key to assign to your Smart Proxy during registration. The activation key attaches a lifecycle environment and a content view to the Smart Proxy. For more information, see Creating an activation key by using Foreman web UI in Managing content.
-
-
Prerequisites for HTTP proxy and network:
-
The Foreman server base operating system must be able to resolve the host name of the Smart Proxy base operating system and vice versa.
-
Ensure HTTPS connection using client certificate authentication is possible between Smart Proxy server and Foreman server. HTTP proxies between Smart Proxy server and Foreman server are not supported.
-
You must configure the host and network-based firewalls accordingly. For more information, see Opening required ports in Installing a Smart Proxy Server nightly on Enterprise Linux.
-
2.1.2. Registering a host to Foreman by using Foreman web UI
You can register a host to Foreman by using the Foreman web UI with registration templates. During the registration process, you can set up various integration features and host tools.
-
Your Foreman account has the Register hosts role assigned or a role with equivalent permissions.
-
Root privileges are available on the host that you want to register.
-
Either
curlorwgetis installed on the host that you want to register. -
Your host is configured for registration. For more information, see Configuring a host for registration in Managing hosts.
-
An activation key must be available for your host. For more information, see Managing Activation Keys in Managing content.
-
Foreman Client repository for the operating system version of the host is synchronized on Foreman server and enabled in the activation key you use. For more information, see Adding content to Foreman in Managing content. This repository is required for the remote execution pull client, OpenVox agent, Tracer, and other tools.
-
If you want to use Smart Proxy servers instead of your Foreman server, ensure that you have configured your Smart Proxy servers accordingly.
ImportantIt is essential to add your Smart Proxy server to the list of trusted proxies on Foreman server!
For more information, see Configuring Smart Proxy server for host registration and provisioning in Installing a Smart Proxy Server nightly on Enterprise Linux.
-
If your Foreman server or Smart Proxy server is behind an HTTP proxy, Subscription Manager on your host is configured to use the HTTP proxy for connection.
-
You have configured the operating system entry on Foreman for Enterprise Linux.
-
In the Foreman web UI, navigate to Hosts > Register Host.
-
Enter the details for how you want the registered host to be configured.
-
If you select a host group from the Host Group list, the following fields inherit their values from the host group:
-
Operating system
-
Activation Keys
-
Lifecycle environment
-
-
A Smart Proxy behind a load balancer takes precedence over the Smart Proxy selected in the Foreman web UI as the content source of the host.
-
-
On the General tab, in the Activation Keys field, enter one or more activation keys to assign to your host.
-
Specify any other registration details that you require. The available settings include the following:
-
On the General tab, in the Smart Proxy field, you can select the Smart Proxy to register your host through. A Smart Proxy behind a load balancer takes precedence over a Smart Proxy selected in the Foreman web UI as the content source of the host.
-
On the General tab, in the Download utility field, you can select
wgetif you want to register your host by using awgetcommand. By default, Foreman generates acurlcommand. -
On the General tab, you can select the Insecure option to make the first call insecure. During this first call, your host downloads the CA file from Foreman. Your host will use this CA file to connect to Foreman with all future calls making them secure.
ImportantInsecure calls expose your hosts to man-in-the-middle attacks.
If an attacker, located in the network between Foreman and your host, fetches the CA file from the first insecure call, the attacker will be able to access the content of the API calls to and from your host and the JSON Web Tokens (JWT). Therefore, if you have chosen to deploy SSH keys during registration, the attacker will be able to access your host using the SSH key.
-
On the Advanced tab, in the Repositories field, you can list repositories to be added before the registration is performed. You do not have to specify repositories if you provide them in an activation key.
-
On the Advanced tab, you can configure remote execution, Insights, and packages to be installed.
-
On the Advanced tab, in the Token lifetime (hours) field, you can change the validity duration of the JSON Web Token (JWT) that Foreman uses for authentication. The duration of this token defines how long the generated registration command works.
Note that Foreman applies the permissions of the user who generates the registration command to authorization of your host. If the user loses or gains additional permissions, the permissions of the JWT change too. Therefore, do not delete, block, or change permissions of the user during the token duration.
The scope of the JWTs is limited to the registration endpoints only and cannot be used anywhere else.
-
On the Advanced tab, you can enable container and Flatpak registry access without a username or password by selecting the Set up container registry certs checkbox. Using certificate-based authentication also enforces lifecycle management of container and Flatpak content for the host.
-
-
Click Generate to create the registration command.
-
Click on the files icon to copy the command to your clipboard.
-
Connect to your host using SSH and run the registration command.
-
Run the registration command as
rooton the host that you want to register. After registration completes, any Ansible roles assigned to a host group you specified when configuring the registration template will run on the host.
-
If your activation key was supposed to enable repositories, verify that the repositories have been enabled:
-
On Enterprise Linux: Check the
/etc/yum.repos.d/redhat.repofile and ensure that the appropriate repositories have been enabled. -
On Debian/Ubuntu: Check the
/etc/apt/sources.listfile and ensure that the appropriate repositories have been enabled. -
On openSUSE/SUSE Linux Enterprise Server: Check the
/etc/zypp/repos.d/directory and ensure that the appropriate repositories have been enabled.
-
2.1.3. Registering a host to Foreman by using Hammer CLI
You can register a host to Foreman by using Hammer CLI with registration templates. During the registration process, you can set up various integration features and host tools.
-
Your Foreman account has the Register hosts role assigned or a role with equivalent permissions.
-
Root privileges are available on the host that you want to register.
-
Either
curlorwgetis installed on the host that you want to register. -
Your host is configured for registration. For more information, see Configuring a host for registration in Managing hosts.
-
An activation key must be available for your host. For more information, see Managing Activation Keys in Managing content.
-
Foreman Client repository for the operating system version of the host is synchronized on Foreman server and enabled in the activation key you use. For more information, see Adding content to Foreman in Managing content. This repository is required for the remote execution pull client, OpenVox agent, Tracer, and other tools.
-
If you want to use Smart Proxy servers instead of your Foreman server, ensure that you have configured your Smart Proxy servers accordingly.
ImportantIt is essential to add your Smart Proxy server to the list of trusted proxies on Foreman server!
For more information, see Configuring Smart Proxy server for host registration and provisioning in Installing a Smart Proxy Server nightly on Enterprise Linux.
-
If your Foreman server or Smart Proxy server is behind an HTTP proxy, Subscription Manager on your host is configured to use the HTTP proxy for connection.
-
You have configured the operating system entry on Foreman for Enterprise Linux.
-
Generate the host registration command:
$ hammer host-registration generate-command \
--activation-keys "My_Activation_Key"
If your hosts do not trust the SSL certificate of Foreman server, append
--insecure trueto disable SSL validation.For more information, see the Hammer CLI help with
hammer host-registration generate-command --help. -
Connect to your host using SSH and run the registration command as
root.
-
If your activation key was supposed to enable repositories, verify that the repositories have been enabled:
-
On Enterprise Linux: Check the
/etc/yum.repos.d/redhat.repofile and ensure that the appropriate repositories have been enabled. -
On Debian/Ubuntu: Check the
/etc/apt/sources.listfile and ensure that the appropriate repositories have been enabled. -
On openSUSE/SUSE Linux Enterprise Server: Check the
/etc/zypp/repos.d/directory and ensure that the appropriate repositories have been enabled.
-
2.1.4. Registering a host to Foreman by using Foreman API
You can register a host to Foreman by using Foreman API with registration templates. During the registration process, you can set up various integration features and host tools.
-
Your Foreman account has the Register hosts role assigned or a role with equivalent permissions.
-
Root privileges are available on the host that you want to register.
-
Either
curlorwgetis installed on the host that you want to register. -
Your host is configured for registration. For more information, see Configuring a host for registration in Managing hosts.
-
An activation key must be available for your host. For more information, see Managing Activation Keys in Managing content.
-
Foreman Client repository for the operating system version of the host is synchronized on Foreman server and enabled in the activation key you use. For more information, see Adding content to Foreman in Managing content. This repository is required for the remote execution pull client, OpenVox agent, Tracer, and other tools.
-
If you want to use Smart Proxy servers instead of your Foreman server, ensure that you have configured your Smart Proxy servers accordingly.
ImportantIt is essential to add your Smart Proxy server to the list of trusted proxies on Foreman server!
For more information, see Configuring Smart Proxy server for host registration and provisioning in Installing a Smart Proxy Server nightly on Enterprise Linux.
-
If your Foreman server or Smart Proxy server is behind an HTTP proxy, Subscription Manager on your host is configured to use the HTTP proxy for connection.
-
You have configured the operating system entry on Foreman for Enterprise Linux.
-
Generate the host registration command using the Foreman API:
$ curl \
--data '{ "registration_command": { "activation_keys": ["My_Activation_Key_1, My_Activation_Key_2"] }}' \
--header 'Content-Type: application/json' \
--request POST \
--user "My_User_Name" \
https://foreman.example.com/api/registration_commands
If your hosts do not trust the SSL certificate of Foreman server, you can disable SSL validation by adding the
--insecureflag to the registration command.$ curl \ --data '{ "registration_command": { "activation_keys": ["My_Activation_Key_1, My_Activation_Key_2"], "insecure": true }}' \ --header 'Content-Type: application/json' \ --request POST \ --user "My_User_Name" \ https://foreman.example.com/api/registration_commandsUse an activation key to simplify specifying the environments.
To enter a password as a command line argument, use
username:passwordsyntax. Keep in mind this can save the password in the shell history. Alternatively, you can use a temporary personal access token instead of a password. To generate a token in the Foreman web UI, navigate to My Account > Personal Access Tokens. -
Connect to your host using SSH and run the registration command.
-
If your activation key was supposed to enable repositories, verify that the repositories have been enabled:
-
On Enterprise Linux: Check the
/etc/yum.repos.d/redhat.repofile and ensure that the appropriate repositories have been enabled. -
On Debian/Ubuntu: Check the
/etc/apt/sources.listfile and ensure that the appropriate repositories have been enabled. -
On openSUSE/SUSE Linux Enterprise Server: Check the
/etc/zypp/repos.d/directory and ensure that the appropriate repositories have been enabled.
-
2.2. Configuring repositories
Enable the necessary repositories on your Foreman host to access installation packages and dependencies.
-
Clear any metadata:
# dnf clean all
-
Install the
foreman-release.rpmpackage:# dnf install https://yum.theforeman.org/releases/nightly/el9/x86_64/foreman-release.rpm
-
Install the
katello-repos-latest.rpmpackage:# dnf install https://yum.theforeman.org/katello/nightly/katello/el9/x86_64/katello-repos-latest.rpm
-
Install the
openvox-releasepackage:# dnf install https://yum.voxpupuli.org/openvox8-release-el-9.noarch.rpm
-
Verify that the required repositories are enabled:
# dnf repolist enabled
3. Configuring Smart Proxy servers with default SSL certificates for load balancing
You can configure one or more Smart Proxy servers that use default SSL certificates for load balancing.
3.1. Configuring Smart Proxy server with default SSL certificates for load balancing without Puppet
On each Smart Proxy server that you want to configure for load balancing, install Katello certificates.
-
Prepare a new Smart Proxy server to use for load balancing. See Preparing Smart Proxy servers for load balancing.
-
Review Services and features supported in a load-balanced setup.
-
On Foreman server, generate Katello certificates for Smart Proxy server:
# foreman-proxy-certs-generate \
--certs-tar "/root/smartproxy.example.com-certs.tar" \
--foreman-proxy-cname loadbalancer.example.com \
--foreman-proxy-fqdn smartproxy.example.com
Retain a copy of the example
foreman-installercommand that is output by theforeman-proxy-certs-generatecommand for installing Smart Proxy server certificate. -
Copy the certificate archive file from Foreman server to Smart Proxy server.
# scp /root/smartproxy.example.com-certs.tar root@smartproxy.example.com:/root/smartproxy.example.com-certs.tar
-
Append the following options to the
foreman-installercommand that you obtain from the output of theforeman-proxy-certs-generatecommand:--certs-cname "loadbalancer.example.com" \ --enable-foreman-proxy-plugin-remote-execution-script
-
On Smart Proxy server, enter the
foreman-installercommand:# foreman-installer --scenario foreman-proxy-content \ --certs-cname "loadbalancer.example.com" \ --certs-tar-file "smartproxy.example.com-certs.tar" \ --enable-foreman-proxy-plugin-remote-execution-script \ --foreman-proxy-foreman-base-url "https://foreman.example.com" \ --foreman-proxy-oauth-consumer-key "oauth key" \ --foreman-proxy-oauth-consumer-secret "oauth secret" \ --foreman-proxy-trusted-hosts "foreman.example.com" \ --foreman-proxy-trusted-hosts "smartproxy.example.com"
4. Configuring Smart Proxy servers with custom SSL certificates for load balancing
You can configure one or more Smart Proxy servers that use custom SSL certificates for load balancing. To do this, configure and install certificates on each Smart Proxy server you want to use for load balancing.
4.1. Creating a custom SSL certificate for Smart Proxy server
On each Smart Proxy server you want to configure for load balancing, create a configuration file for the Certificate Signing Request and include the load balancer and Smart Proxy server as Subject Alternative Names (SAN).
-
To store all the source certificate files, create a directory that is accessible only to the
rootuser:# mkdir /root/smart-proxy_cert
-
Create a private key with which to sign the certificate signing request (CSR). The private key must be unencrypted:
# openssl genrsa -out /root/smart-proxy_cert/smart-proxy_cert_key.pem 4096
If you already have a private key, skip this step.
-
Optional: Verify that the key is unencrypted:
# openssl pkey -noout -in /root/smart-proxy_cert/smart-proxy_cert_key.pem
If the command does not ask for a password, the key is unencrypted. If your private key is password-protected, remove the password.
-
Create the
/root/smart-proxy_cert/openssl.cnfconfiguration file for the CSR and include the following content:[ req ] req_extensions = v3_req distinguished_name = req_distinguished_name x509_extensions = usr_cert prompt = no [ req_distinguished_name ] commonName = smartproxy.example.com [ v3_req ] basicConstraints = CA:FALSE keyUsage = digitalSignature, keyEncipherment extendedKeyUsage = serverAuth, clientAuth subjectAltName = @alt_names [alt_names] DNS.1 = loadbalancer.example.com DNS.2 = smartproxy.example.com
The options used in the configuration file include the following:
commonName-
The certificate common name. It must match the FQDN of Smart Proxy server. Ensure to change this when running the command on each Smart Proxy server that you configure for load balancing. You can also set a wildcard value
*. [alt_names]-
The alternative names for the load balancer and Smart Proxy server. Include the FQDN of the load balancer as
DNS.1and the FQDN of Smart Proxy server asDNS.2.For more information about the
[ v3_req ]parameters and their purpose, see RFC 5280: Internet X.509 Public Key Infrastructure Certificate and Certificate Revocation List (CRL) Profile.
-
Optional: If you want to add Distinguished Name (DN) details to the CSR, add the following information to the
[ req_distinguished_name ]section:[req_distinguished_name] commonName = smartproxy.example.com countryName = My_Country_Name stateOrProvinceName = My_State_Or_Province_Name localityName = My_Locality_Name organizationName = My_Organization_Or_Company_Name organizationalUnitName = My_Organizational_Unit_Name
The options used in the configuration file include the following:
countryName-
The country represented by a two-letter code
stateOrProvinceName-
Full name of the state or province
localityName-
Full name of the locality (example: New York)
organizationalUnitName-
Division responsible for the certificate (example: IT department)
-
Generate the CSR:
# openssl req -new \
-key /root/smart-proxy_cert/smart-proxy_cert_key.pem \
-config /root/smart-proxy_cert/openssl.cnf \
-out /root/smart-proxy_cert/smart-proxy_cert_csr.pem
The options used in the configuration file include the following:
-key-
Path to the private key
-config-
Path to the configuration file
-out-
Path to the CSR to generate
-
Send the certificate signing request to the certificate authority (CA). The same CA must sign certificates for Foreman server and Smart Proxy server.
When you submit the request, specify the lifespan of the certificate. The method for sending the certificate request varies, so consult the CA for the preferred method. In response to the request, you can expect to receive a CA bundle and a signed certificate, in separate files.
-
Copy the Certificate Authority bundle and Smart Proxy server certificate file that you receive from the Certificate Authority, and Smart Proxy server private key to your Foreman server.
4.2. Configuring Smart Proxy server with custom SSL certificates for load balancing without Puppet
On each Smart Proxy server you want to configure for load balancing, install Katello certificates.
-
Prepare a new Smart Proxy server to use for load balancing. See Preparing Smart Proxy servers for load balancing.
-
Review Services and features supported in a load-balanced setup.
-
On Foreman server, enter the
foreman-proxy-certs-generatecommand to generate Smart Proxy certificates:# foreman-proxy-certs-generate \ --certs-tar /root/smart-proxy_cert/smart-proxy.tar \ --foreman-proxy-cname loadbalancer.example.com \ --foreman-proxy-fqdn smartproxy.example.com \ --server-ca-cert /root/smart-proxy_cert/ca_cert_bundle.pem \ --server-cert /root/smart-proxy_cert/smart-proxy.pem \ --server-key /root/smart-proxy_cert/smart-proxy.pem
Retain a copy of the example
foreman-installercommand from the output for installing Smart Proxy server certificates. -
Copy the certificate archive file from Foreman server to Smart Proxy server:
# scp /root/smartproxy.example.com-certs.tar root@smartproxy.example.com:smartproxy.example.com-certs.tar
-
Append the following options to the
foreman-installercommand that you obtain from the output of theforeman-proxy-certs-generatecommand:--certs-cname "loadbalancer.example.com" \ --enable-foreman-proxy-plugin-remote-execution-script
-
On Smart Proxy server, enter the
foreman-installercommand:# foreman-installer --scenario foreman-proxy-content \ --certs-cname "loadbalancer.example.com" \ --certs-tar-file "smartproxy.example.com-certs.tar" \ --enable-foreman-proxy-plugin-remote-execution-script \ --foreman-proxy-foreman-base-url "https://foreman.example.com" \ --foreman-proxy-oauth-consumer-key "oauth key" \ --foreman-proxy-oauth-consumer-secret "oauth secret" \ --foreman-proxy-trusted-hosts "foreman.example.com" \ --foreman-proxy-trusted-hosts "smartproxy.example.com"
5. Configuring Smart Proxy servers with default SSL certificates for load balancing (with Puppet)
If you use Puppet in your Foreman setup, you can configure one or more Smart Proxy servers that use default SSL certificates for load balancing.
To do this, you configure Puppet certificate signing on one of your Smart Proxy servers. Then, you configure each remaining Puppet Smart Proxy used for load balancing to use the certificates. The first Smart Proxy server will generate and sign Puppet certificates for the remaining Smart Proxies configured for load balancing.
5.1. Configuring Smart Proxy server with default SSL certificates to generate and sign Puppet certificates
On the Smart Proxy server that will generate Puppet certificates for all other load-balancing Smart Proxy servers, configure Puppet certificate generation and signing.
-
Prepare a new Smart Proxy server to use for load balancing. See Preparing Smart Proxy servers for load balancing.
-
Review Services and features supported in a load-balanced setup.
-
On Foreman server, generate Katello certificates for the system where you configure Smart Proxy server to generate and sign Puppet certificates:
# foreman-proxy-certs-generate \
--certs-tar "/root/smart-proxy-ca.example.com-certs.tar" \
--foreman-proxy-cname loadbalancer.example.com \
--foreman-proxy-fqdn smart-proxy-ca.example.com
Retain a copy of the example
foreman-installercommand that is output by theforeman-proxy-certs-generatecommand for installing Smart Proxy server certificate. -
Copy the certificate archive file from Foreman server to Smart Proxy server:
# scp /root/smart-proxy-ca.example.com-certs.tar root@smart-proxy-ca.example.com:smart-proxy-ca.example.com-certs.tar
-
Append the following options to the
foreman-installercommand that you obtain from the output of theforeman-proxy-certs-generatecommand:--certs-cname "loadbalancer.example.com" \ --enable-foreman-proxy-plugin-remote-execution-script \ --foreman-proxy-puppetca "true" \ --puppet-ca-server "smart-proxy-ca.example.com" \ --puppet-dns-alt-names "loadbalancer.example.com" \ --puppet-server-ca "true"
-
On Smart Proxy server, enter the
foreman-installercommand:# foreman-installer --scenario foreman-proxy-content \ --certs-cname "loadbalancer.example.com" \ --certs-tar-file "smart-proxy-ca.example.com-certs.tar" \ --enable-foreman-proxy-plugin-remote-execution-script \ --enable-puppet \ --foreman-proxy-foreman-base-url "https://foreman.example.com" \ --foreman-proxy-oauth-consumer-key "oauth key" \ --foreman-proxy-oauth-consumer-secret "oauth secret" \ --foreman-proxy-puppetca "true" \ --foreman-proxy-trusted-hosts "foreman.example.com" \ --foreman-proxy-trusted-hosts "smart-proxy-ca.example.com" \ --puppet-ca-server "smart-proxy-ca.example.com" \ --puppet-dns-alt-names "loadbalancer.example.com" \ --puppet-server true \ --puppet-server-ca "true"
-
On Smart Proxy server that is the Puppet Certificate Authority, stop the OpenVox server:
# systemctl stop puppetserver
-
Generate Puppet certificates for all other Smart Proxy servers that you configure for load balancing, except the system where you first configured Puppet certificate signing:
# puppetserver ca generate \
--ca-client \
--certname smartproxy.example.com \
--subject-alt-names loadbalancer.example.com
This command creates the following files:
-
/etc/puppetlabs/puppet/ssl/certs/smartproxy.example.com.pem -
/etc/puppetlabs/puppet/ssl/private_keys/smartproxy.example.com.pem -
/etc/puppetlabs/puppet/ssl/public_keys/smartproxy.example.com.pem -
/etc/puppetlabs/puppetserver/ca/signed/smartproxy.example.com.pem
-
-
Start the OpenVox server:
# systemctl start puppetserver
5.2. Configuring remaining Smart Proxy servers with default SSL certificates for load balancing
On each load-balancing Smart Proxy server, excluding the Smart Proxy server configured to sign Puppet certificates, configure the system to use Puppet certificates.
-
On Foreman server, generate Katello certificates for Smart Proxy server:
# foreman-proxy-certs-generate \
--certs-tar "/root/smartproxy.example.com-certs.tar" \
--foreman-proxy-cname loadbalancer.example.com \
--foreman-proxy-fqdn smartproxy.example.com
Retain a copy of the example
foreman-installercommand that is output by theforeman-proxy-certs-generatecommand for installing Smart Proxy server certificate. -
Copy the certificate archive file from Foreman server to Smart Proxy server:
# scp /root/smartproxy.example.com-certs.tar root@smartproxy.example.com:/root/smartproxy.example.com-certs.tar
-
On Smart Proxy server, install the
puppetserverpackage:# dnf install puppetserver
-
On Smart Proxy server, create directories for puppet certificates:
# mkdir -p /etc/puppetlabs/puppet/ssl/certs/ \
/etc/puppetlabs/puppet/ssl/private_keys/ \
/etc/puppetlabs/puppet/ssl/public_keys/
-
On Smart Proxy server, copy the Puppet certificates for this Smart Proxy server from the system where you configure Smart Proxy server to sign Puppet certificates:
# scp root@smart-proxy-ca.example.com:/etc/puppetlabs/puppet/ssl/certs/smartproxy.example.com.pem /etc/puppetlabs/puppet/ssl/certs/smartproxy.example.com.pem
# scp root@smart-proxy-ca.example.com:/etc/puppetlabs/puppet/ssl/certs/ca.pem /etc/puppetlabs/puppet/ssl/certs/ca.pem
# scp root@smart-proxy-ca.example.com:/etc/puppetlabs/puppet/ssl/private_keys/smartproxy.example.com.pem /etc/puppetlabs/puppet/ssl/private_keys/smartproxy.example.com.pem
# scp root@smart-proxy-ca.example.com:/etc/puppetlabs/puppet/ssl/public_keys/smartproxy.example.com.pem /etc/puppetlabs/puppet/ssl/public_keys/smartproxy.example.com.pem
-
On Smart Proxy server, change the
/etc/puppetlabs/puppet/ssl/directory ownership to userpuppetand grouppuppet:# chown -R puppet:puppet /etc/puppetlabs/puppet/ssl/
-
On Smart Proxy server, set the SELinux context for the
/etc/puppetlabs/puppet/ssl/directory:# restorecon -Rv /etc/puppetlabs/puppet/ssl/
-
Append the following options to the
foreman-installercommand that you obtain from the output of theforeman-proxy-certs-generatecommand:--certs-cname "loadbalancer.example.com" \ --enable-foreman-proxy-plugin-remote-execution-script \ --foreman-proxy-puppetca "false" \ --puppet-ca-server "smart-proxy-ca.example.com" \ --puppet-dns-alt-names "loadbalancer.example.com" \ --puppet-server-ca "false"
-
On Smart Proxy server, enter the
foreman-installercommand:# foreman-installer --scenario foreman-proxy-content \ --certs-cname "loadbalancer.example.com" \ --certs-tar-file "smartproxy.example.com-certs.tar" \ --enable-foreman-proxy-plugin-remote-execution-script \ --foreman-proxy-foreman-base-url "https://foreman.example.com" \ --foreman-proxy-oauth-consumer-key "oauth key" \ --foreman-proxy-oauth-consumer-secret "oauth secret" \ --foreman-proxy-puppetca "false" \ --foreman-proxy-trusted-hosts "foreman.example.com" \ --foreman-proxy-trusted-hosts "smartproxy.example.com" \ --puppet-ca-server "smart-proxy-ca.example.com" \ --puppet-dns-alt-names "loadbalancer.example.com" \ --puppet-server-ca "false"
5.3. Managing Puppet limitations with load balancing in Foreman
If you use Puppet, Puppet certificate signing is assigned to the first Smart Proxy that you configure. If the first Smart Proxy is down, hosts cannot obtain Puppet content.
Puppet Certificate Authority (CA) management does not support certificate signing in a load-balanced setup. Puppet CA stores certificate information, such as the serial number counter and CRL, on the file system. Multiple writer processes that attempt to use the same data can corrupt it.
To manage this Puppet limitation, complete the following steps:
-
Configure Puppet certificate signing on one Smart Proxy server, typically the first system where you configure Smart Proxy server for load balancing.
-
Configure the clients to send CA requests to port 8141 on a load balancer.
-
Configure a load balancer to redirect CA requests from port 8141 to port 8140 on the system where you configure Smart Proxy server to sign Puppet certificates.
To troubleshoot issues, reproduce the issue on each Smart Proxy, bypassing the load balancer. This solution does not use Pacemaker or other similar HA tools to maintain one state across all Smart Proxies.
6. Configuring Smart Proxy servers with custom SSL certificates for load balancing (with Puppet)
You can configure one or more Smart Proxy servers that use custom SSL certificates for load balancing.
6.1. Creating a custom SSL certificate for Smart Proxy server
On each Smart Proxy server you want to configure for load balancing, create a configuration file for the Certificate Signing Request and include the load balancer and Smart Proxy server as Subject Alternative Names (SAN).
-
To store all the source certificate files, create a directory that is accessible only to the
rootuser:# mkdir /root/smart-proxy_cert
-
Create a private key with which to sign the certificate signing request (CSR). The private key must be unencrypted:
# openssl genrsa -out /root/smart-proxy_cert/smart-proxy_cert_key.pem 4096
If you already have a private key, skip this step.
-
Optional: Verify that the key is unencrypted:
# openssl pkey -noout -in /root/smart-proxy_cert/smart-proxy_cert_key.pem
If the command does not ask for a password, the key is unencrypted. If your private key is password-protected, remove the password.
-
Create the
/root/smart-proxy_cert/openssl.cnfconfiguration file for the CSR and include the following content:[ req ] req_extensions = v3_req distinguished_name = req_distinguished_name x509_extensions = usr_cert prompt = no [ req_distinguished_name ] commonName = smartproxy.example.com [ v3_req ] basicConstraints = CA:FALSE keyUsage = digitalSignature, keyEncipherment extendedKeyUsage = serverAuth, clientAuth subjectAltName = @alt_names [alt_names] DNS.1 = loadbalancer.example.com DNS.2 = smartproxy.example.com
The options used in the configuration file include the following:
commonName-
The certificate common name. It must match the FQDN of Smart Proxy server. Ensure to change this when running the command on each Smart Proxy server that you configure for load balancing. You can also set a wildcard value
*. [alt_names]-
The alternative names for the load balancer and Smart Proxy server. Include the FQDN of the load balancer as
DNS.1and the FQDN of Smart Proxy server asDNS.2.For more information about the
[ v3_req ]parameters and their purpose, see RFC 5280: Internet X.509 Public Key Infrastructure Certificate and Certificate Revocation List (CRL) Profile.
-
Optional: If you want to add Distinguished Name (DN) details to the CSR, add the following information to the
[ req_distinguished_name ]section:[req_distinguished_name] commonName = smartproxy.example.com countryName = My_Country_Name stateOrProvinceName = My_State_Or_Province_Name localityName = My_Locality_Name organizationName = My_Organization_Or_Company_Name organizationalUnitName = My_Organizational_Unit_Name
The options used in the configuration file include the following:
countryName-
The country represented by a two-letter code
stateOrProvinceName-
Full name of the state or province
localityName-
Full name of the locality (example: New York)
organizationalUnitName-
Division responsible for the certificate (example: IT department)
-
Generate the CSR:
# openssl req -new \
-key /root/smart-proxy_cert/smart-proxy_cert_key.pem \
-config /root/smart-proxy_cert/openssl.cnf \
-out /root/smart-proxy_cert/smart-proxy_cert_csr.pem
The options used in the configuration file include the following:
-key-
Path to the private key
-config-
Path to the configuration file
-out-
Path to the CSR to generate
-
Send the certificate signing request to the certificate authority (CA). The same CA must sign certificates for Foreman server and Smart Proxy server.
When you submit the request, specify the lifespan of the certificate. The method for sending the certificate request varies, so consult the CA for the preferred method. In response to the request, you can expect to receive a CA bundle and a signed certificate, in separate files.
-
Copy the Certificate Authority bundle and Smart Proxy server certificate file that you receive from the Certificate Authority, and Smart Proxy server private key to your Foreman server.
6.2. Configuring Smart Proxy server with custom SSL certificates to generate and sign Puppet certificates
On the Smart Proxy server that will generate Puppet certificates for all other load-balancing Smart Proxy servers, configure Puppet certificate generation and signing.
-
Prepare a new Smart Proxy server to use for load balancing. See Preparing Smart Proxy servers for load balancing.
-
Review Services and features supported in a load-balanced setup.
-
On Foreman server, enter the
foreman-proxy-certs-generatecommand to generate Smart Proxy certificates:# foreman-proxy-certs-generate \ --certs-tar /root/smart-proxy_cert/smart-proxy-ca.tar \ --foreman-proxy-cname loadbalancer.example.com \ --foreman-proxy-fqdn smart-proxy-ca.example.com \ --server-ca-cert /root/smart-proxy_cert/ca_cert_bundle.pem \ --server-cert /root/smart-proxy_cert/smart-proxy-ca.pem \ --server-key /root/smart-proxy_cert/smart-proxy-ca.pem
Retain a copy of the example
foreman-installercommand from the output for installing Smart Proxy server certificates. -
Copy the certificate archive file from Foreman server to Smart Proxy server.
-
Append the following options to the
foreman-installercommand that you obtain from the output of theforeman-proxy-certs-generatecommand:--enable-foreman-proxy-plugin-remote-execution-script \ --foreman-proxy-puppetca "true" \ --puppet-ca-server "smart-proxy-ca.example.com" \ --puppet-dns-alt-names "loadbalancer.example.com" \ --puppet-server-ca "true"
-
On Smart Proxy server, enter the
foreman-installercommand:# foreman-installer --scenario foreman-proxy-content \ --certs-cname "loadbalancer.example.com" \ --certs-tar-file "certs.tgz" \ --enable-foreman-proxy-plugin-remote-execution-script \ --enable-puppet \ --foreman-proxy-foreman-base-url "https://foreman.example.com" \ --foreman-proxy-oauth-consumer-key "oauth key" \ --foreman-proxy-oauth-consumer-secret "oauth secret" \ --foreman-proxy-puppetca "true" \ --foreman-proxy-trusted-hosts "foreman.example.com" \ --foreman-proxy-trusted-hosts "smart-proxy-ca.example.com" \ --puppet-ca-server "smart-proxy-ca.example.com" \ --puppet-dns-alt-names "loadbalancer.example.com" \ --puppet-server true \ --puppet-server-ca "true"
-
On Smart Proxy server that is the Puppetserver Certificate Authority, stop the OpenVox server:
# systemctl stop puppetserver
-
Generate Puppet certificates for all other Smart Proxy servers that you configure for load balancing, except the system where you first configured Puppet certificate signing:
# puppetserver ca generate \
--ca-client \
--certname smartproxy.example.com \
--subject-alt-names loadbalancer.example.com
This command creates the following files:
-
/etc/puppetlabs/puppet/ssl/certs/smartproxy.example.com.pem -
/etc/puppetlabs/puppet/ssl/private_keys/smartproxy.example.com.pem -
/etc/puppetlabs/puppet/ssl/public_keys/smartproxy.example.com.pem -
/etc/puppetlabs/puppetserver/ca/signed/smartproxy.example.com.pem
-
-
Start the OpenVox server:
# systemctl start puppetserver
6.3. Configuring remaining Smart Proxy servers with custom SSL certificates for load balancing
On each load-balancing Smart Proxy server, excluding the Smart Proxy server configured to sign Puppet certificates, configure the system to use Puppet certificates.
-
On Foreman server, enter the
foreman-proxy-certs-generatecommand to generate Smart Proxy certificates:# foreman-proxy-certs-generate \ --certs-tar /root/smart-proxy_cert/smart-proxy.tar \ --foreman-proxy-cname loadbalancer.example.com \ --foreman-proxy-fqdn smartproxy.example.com \ --server-ca-cert /root/smart-proxy_cert/ca_cert_bundle.pem \ --server-cert /root/smart-proxy_cert/smart-proxy.pem \ --server-key /root/smart-proxy_cert/smart-proxy.pem
Retain a copy of the example
foreman-installercommand from the output for installing Smart Proxy server certificates. -
Copy the certificate archive file from Foreman server to Smart Proxy server.
# scp /root/smartproxy.example.com-certs.tar root@smartproxy.example.com:smartproxy.example.com-certs.tar
-
On Smart Proxy server, install the
puppetserverpackage:# dnf install puppetserver
-
On Smart Proxy server, create directories for puppet certificates:
# mkdir -p /etc/puppetlabs/puppet/ssl/certs/ \
/etc/puppetlabs/puppet/ssl/private_keys/ \
/etc/puppetlabs/puppet/ssl/public_keys/
-
On Smart Proxy server, copy the Puppet certificates for this Smart Proxy server from the system where you configure Smart Proxy server to sign Puppet certificates:
# scp root@smart-proxy-ca.example.com:/etc/puppetlabs/puppet/ssl/certs/smartproxy.example.com.pem /etc/puppetlabs/puppet/ssl/certs/smartproxy.example.com.pem
# scp root@smart-proxy-ca.example.com:/etc/puppetlabs/puppet/ssl/certs/ca.pem /etc/puppetlabs/puppet/ssl/certs/ca.pem
# scp root@smart-proxy-ca.example.com:/etc/puppetlabs/puppet/ssl/private_keys/smartproxy.example.com.pem /etc/puppetlabs/puppet/ssl/private_keys/smartproxy.example.com.pem
# scp root@smart-proxy-ca.example.com:/etc/puppetlabs/puppet/ssl/public_keys/smartproxy.example.com.pem /etc/puppetlabs/puppet/ssl/public_keys/smartproxy.example.com.pem
-
On Smart Proxy server, change the
/etc/puppetlabs/puppet/ssl/directory ownership to userpuppetand grouppuppet:# chown -R puppet:puppet /etc/puppetlabs/puppet/ssl/
-
On Smart Proxy server, set the SELinux context for the
/etc/puppetlabs/puppet/ssl/directory:# restorecon -Rv /etc/puppetlabs/puppet/ssl/
-
Append the following options to the
foreman-installercommand that you obtain from the output of theforeman-proxy-certs-generatecommand:--certs-cname "loadbalancer.example.com" \ --enable-foreman-proxy-plugin-remote-execution-script \ --foreman-proxy-puppetca "false" \ --puppet-ca-server "smart-proxy-ca.example.com" \ --puppet-dns-alt-names "loadbalancer.example.com" \ --puppet-server-ca "false"
-
On Smart Proxy server, enter the
foreman-installercommand:# foreman-installer --scenario foreman-proxy-content \ --certs-cname "loadbalancer.example.com" \ --certs-tar-file "smartproxy.example.com-certs.tar" \ --enable-foreman-proxy-plugin-remote-execution-script \ --foreman-proxy-foreman-base-url "https://foreman.example.com" \ --foreman-proxy-oauth-consumer-key "oauth key" \ --foreman-proxy-oauth-consumer-secret "oauth secret" \ --foreman-proxy-puppetca "false" \ --foreman-proxy-trusted-hosts "foreman.example.com" \ --foreman-proxy-trusted-hosts "smartproxy.example.com" \ --puppet-ca-server "smart-proxy-ca.example.com" \ --puppet-dns-alt-names "loadbalancer.example.com" \ --puppet-server-ca "false"
6.4. Managing Puppet limitations with load balancing in Foreman
If you use Puppet, Puppet certificate signing is assigned to the first Smart Proxy that you configure. If the first Smart Proxy is down, hosts cannot obtain Puppet content.
Puppet Certificate Authority (CA) management does not support certificate signing in a load-balanced setup. Puppet CA stores certificate information, such as the serial number counter and CRL, on the file system. Multiple writer processes that attempt to use the same data can corrupt it.
To manage this Puppet limitation, complete the following steps:
-
Configure Puppet certificate signing on one Smart Proxy server, typically the first system where you configure Smart Proxy server for load balancing.
-
Configure the clients to send CA requests to port 8141 on a load balancer.
-
Configure a load balancer to redirect CA requests from port 8141 to port 8140 on the system where you configure Smart Proxy server to sign Puppet certificates.
To troubleshoot issues, reproduce the issue on each Smart Proxy, bypassing the load balancer. This solution does not use Pacemaker or other similar HA tools to maintain one state across all Smart Proxies.
7. Installing and configuring the load balancer
Foreman community provides general guidance for configuring an HAProxy load balancer using Enterprise Linux 9. However, you can install any suitable load balancing software solution that supports TCP forwarding.
7.1. Installing the load balancer
The following example provides general guidance for configuring an HAProxy load balancer using Enterprise Linux 9. However, you can install any suitable load balancing software solution that supports TCP forwarding.
-
Install HAProxy:
# dnf install haproxy
-
Install the following package that includes the
semanagetool:# dnf install policycoreutils-python-utils
-
Configure SELinux to allow HAProxy to bind any port:
# semanage boolean --modify --on haproxy_connect_any
-
Configure the load balancer to balance the network load for the ports as described in Ports configuration for the load balancer.
-
Configure the load balancer to disable SSL offloading and allow client-side SSL certificates to pass through to back end servers. This is required because communication from clients to Smart Proxy servers depends on client-side SSL certificates.
-
Start and enable the HAProxy service:
# systemctl enable --now haproxy
7.2. Ports configuration for the load balancer
You must ensure proper network configuration of the load balancer to enable it to balance the network load for the ports.
For example, to configure ports for HAProxy, edit the /etc/haproxy/haproxy.cfg file to correspond with the table.
| Service | Port | Mode | Balance Mode | Destination |
|---|---|---|---|---|
HTTP |
80 |
TCP |
roundrobin |
port 80 on all Smart Proxy servers |
HTTPS and RHSM |
443 |
TCP |
source |
port 443 on all Smart Proxy servers |
Anaconda for template retrieval |
8000 |
TCP |
roundrobin |
port 8000 on all Smart Proxy servers |
Puppet (Optional) |
8140 |
TCP |
roundrobin |
port 8140 on all Smart Proxy servers |
PuppetCA (Optional) |
8141 |
TCP |
roundrobin |
port 8140 only on the system where you configure Smart Proxy server to sign Puppet certificates |
Smart Proxy HTTPS for Host Registration and optionally OpenSCAP |
9090 |
TCP |
roundrobin |
port 9090 on all Smart Proxy servers |
8. Verifying the load balancing configuration
Verify the load balancing configuration for each Smart Proxy server to ensure content and registration keep working when one server is unavailable.
-
Shut down the base operating system for your Smart Proxy server.
-
Verify that content or subscription management features are available on clients registered to this Smart Proxy. For example, enter the
subscription-manager refreshcommand on a client. -
Restart the base operating system for your Smart Proxy server.
9. Registering clients to the load balancer
To balance the load of network traffic from clients, you must register the clients to the load balancer.
To consume container content from a load balancer regardless of client registration, use the load balancer hostname with the container client of choice.
For example, use podman login loadbalancer.example.com to log in.
9.1. Setting the load balancer for host registration
You can configure Foreman to register clients through a load balancer when using the host registration feature.
You will be able to register hosts to the load balancer instead of Smart Proxy. The load balancer will decide through which Smart Proxy to register the host at the time of request. Upon registration, the subscription manager on the host will be configured to manage content through the load balancer.
-
You configured SSL certificates on all Smart Proxy servers. For more information, see the following sections:
-
Configuring Smart Proxy servers with default SSL certificates for load balancing.
-
Configuring Smart Proxy servers with custom SSL certificates for load balancing.
-
Configuring Smart Proxy servers with default SSL certificates for load balancing (with Puppet).
-
Configuring Smart Proxy servers with custom SSL certificates for load balancing (with Puppet).
-
-
You enabled Registration and Templates plugins on all Smart Proxy servers:
# foreman-installer \
--foreman-proxy-registration true \
--foreman-proxy-templates true
-
On all Smart Proxy servers, set the registration and template URLs using
foreman-installer:# foreman-installer \ --foreman-proxy-registration-url "https://loadbalancer.example.com:9090" \ --foreman-proxy-template-url "http://loadbalancer.example.com:8000"
-
In the Foreman web UI, navigate to Infrastructure > Smart Proxies.
-
For each Smart Proxy, click the dropdown menu in the Actions column and select Refresh.
9.2. Registering a host to the load balancer using Foreman web UI
After setting the load balancer for host registration, you can register a host to the load balancer.
-
In the Foreman web UI, navigate to Hosts > Register Host.
-
From the Smart Proxy dropdown list, select your Smart Proxy server configured for load balancing.
-
Select Force to register a host that has been previously registered to a Smart Proxy server.
-
From the Activation Keys list, select the activation keys to assign to your host.
-
Click Generate to create the registration command.
-
Click on the files icon to copy the command to your clipboard.
-
Connect to your host using SSH and run the registration command.
-
Ensure that the appropriate repositories have been enabled:
-
On Enterprise Linux: Check the
/etc/yum.repos.d/redhat.repofile and ensure that the appropriate repositories have been enabled. -
On Debian/Ubuntu: Check the
/etc/apt/sources.listfile and ensure that the appropriate repositories have been enabled. -
On openSUSE/SUSE Linux Enterprise Server: Check the
/etc/zypp/repos.d/directory and ensure that the appropriate repositories have been enabled.
-
9.3. Registering a host to the load balancer using CLI
After setting the load balancer for host registration, you can register a host to the load balancer.
-
Generate the host registration command using the Hammer CLI:
$ hammer host-registration generate-command \
--activation-keys "My_Activation_Key"
If your hosts do not trust the SSL certificate of Foreman server, you can disable SSL validation by adding the
--insecureflag to the registration command.$ hammer host-registration generate-command \ --activation-keys "My_Activation_Key" \ --insecure true
Include the
--smart-proxy-id My_Smart_Proxy_IDoption. You can use the ID of any Smart Proxy server that you configured for host registration load balancing. Foreman will apply the load balancer to the registration command automatically.Include the
--forceoption to register a host that has been previously registered to a Smart Proxy server. -
Connect to your host using SSH and run the registration command.
-
Ensure that the appropriate repositories have been enabled:
-
On Enterprise Linux: Check the
/etc/yum.repos.d/redhat.repofile and ensure that the appropriate repositories have been enabled. -
On Debian/Ubuntu: Check the
/etc/apt/sources.listfile and ensure that the appropriate repositories have been enabled. -
On openSUSE/SUSE Linux Enterprise Server: Check the
/etc/zypp/repos.d/directory and ensure that the appropriate repositories have been enabled.
-
9.4. Registering a host to the load balancer using API
After setting the load balancer for host registration, you can register a host to a load-balanced Smart Proxy.
-
Generate the host registration command using the Foreman API:
$ curl \
--data '{ "registration_command": { "activation_keys": ["My_Activation_Key_1, My_Activation_Key_2"] }}' \
--header 'Content-Type: application/json' \
--request POST \
--user "My_User_Name:My_Password" \
https://foreman.example.com/api/registration_commands
If your hosts do not trust the SSL certificate of Foreman server, you can disable SSL validation by adding the
--insecureflag to the registration command.$ curl \ --data '{ "registration_command": { "activation_keys": ["My_Activation_Key_1, My_Activation_Key_2"], "insecure": true }}' \ --header 'Content-Type: application/json' \ --insecure \ --request POST \ --user "My_User_Name:My_Password" \ https://foreman.example.com/api/registration_commandsUse an activation key to simplify specifying the environments. For more information, see Managing Activation Keys in Managing content.
Include
{ "smart_proxy_id": My_Smart_Proxy_ID }. You can use the ID of any Smart Proxy server that you configured for host registration load balancing. Foreman will apply the load balancer to the registration command automatically.Include
{ "force": true }to register a host that has been previously registered to a Smart Proxy server.To enter a password as a command line argument, use
username:passwordsyntax. Keep in mind this can save the password in the shell history. Alternatively, you can use a temporary personal access token instead of a password. To generate a token in the Foreman web UI, navigate to My Account > Personal Access Tokens. -
Connect to your host using SSH and run the registration command.
-
Ensure that the appropriate repositories have been enabled:
-
On Enterprise Linux: Check the
/etc/yum.repos.d/redhat.repofile and ensure that the appropriate repositories have been enabled. -
On Debian/Ubuntu: Check the
/etc/apt/sources.listfile and ensure that the appropriate repositories have been enabled. -
On openSUSE/SUSE Linux Enterprise Server: Check the
/etc/zypp/repos.d/directory and ensure that the appropriate repositories have been enabled.
-
10. Propagating SCAP content through the load balancer
If you use OpenSCAP to manage security compliance on your clients, you must configure the SCAP client to send ARF reports to the load balancer instead of Smart Proxy. The configuration procedure depends on the method you have selected to deploy compliance policies.
10.1. Propagating SCAP content using Ansible deployment
Propagate Security Content Automation Protocol (SCAP) content through the load balancer when using Ansible deployment so that compliance reports reach Foreman through the load balancer.
-
Ensure that you have configured Foreman for Ansible deployment of compliance policies. For more information, see Configuring Compliance Policy Deployment Methods in Managing security compliance.
-
In the Foreman web UI, navigate to Configure > Ansible > Variables.
-
Search for the
foreman_scap_client_portvariable and click its name. -
In the Default Behavior area, ensure that the Override checkbox is selected.
-
In the Parameter Type list, ensure that
integeris selected. -
In the Default Value field, enter
9090. -
In the Specify Matchers area, remove all matchers that override the default value.
-
Click Submit.
-
Search for the
foreman_scap_client_servervariable and click its name. -
In the Default Behavior area, ensure that the Override checkbox is selected.
-
In the Parameter Type list, ensure that
stringis selected. -
In the Default Value field, enter the FQDN of your load balancer, such as
loadbalancer.example.com. -
In the Specify Matchers area, remove all matchers that override the default value.
-
Click Submit.
-
Continue with deploying a compliance policy using Ansible. For more information, see:
-
Deploying a Policy in a Host Group Using Ansible in Managing security compliance
-
Deploying a Policy on a Host Using Ansible in Managing security compliance
-
-
On the client, verify that the
/etc/foreman_scap_client/config.yamlfile contains the following lines:# Foreman proxy to which reports should be uploaded :server: 'loadbalancer.example.com' :port: 9090
10.2. Propagating SCAP content using Puppet deployment
Propagate Security Content Automation Protocol (SCAP) content through the load balancer when using Puppet deployment so that compliance reports reach Foreman through the load balancer.
-
Ensure that you have configured Foreman for Puppet deployment of compliance policies. For more information, see Configuring Compliance Policy Deployment Methods in Managing security compliance.
-
In the Foreman web UI, navigate to Configure > Puppet ENC > Classes.
-
Click
foreman_scap_client. -
Click the Smart Class Parameter tab.
-
In the pane to the left of the Smart Class Parameter window, click
port. -
In the Default Behavior area, select the Override checkbox.
-
From the Key Type list, select
integer. -
In the Default Value field, enter
9090. -
In the pane to the left of the Smart Class Parameter window, click
server. -
In the Default Behavior area, select the Override checkbox.
-
From the Key Type list, select
string. -
In the Default Value field, enter the FQDN of your load balancer, such as
loadbalancer.example.com. -
In the lower left of the Smart Class Parameter window, click Submit.
-
Continue with deploying a compliance policy using Puppet. For more information, see:
-
Deploying a Policy in a Host Group Using Puppet in Managing security compliance
-
Deploying a Policy on a Host Using Puppet in Managing security compliance
-
-
On the client, verify that the
/etc/foreman_scap_client/config.yamlfile contains the following lines:# Foreman proxy to which reports should be uploaded :server: 'loadbalancer.example.com' :port: 9090